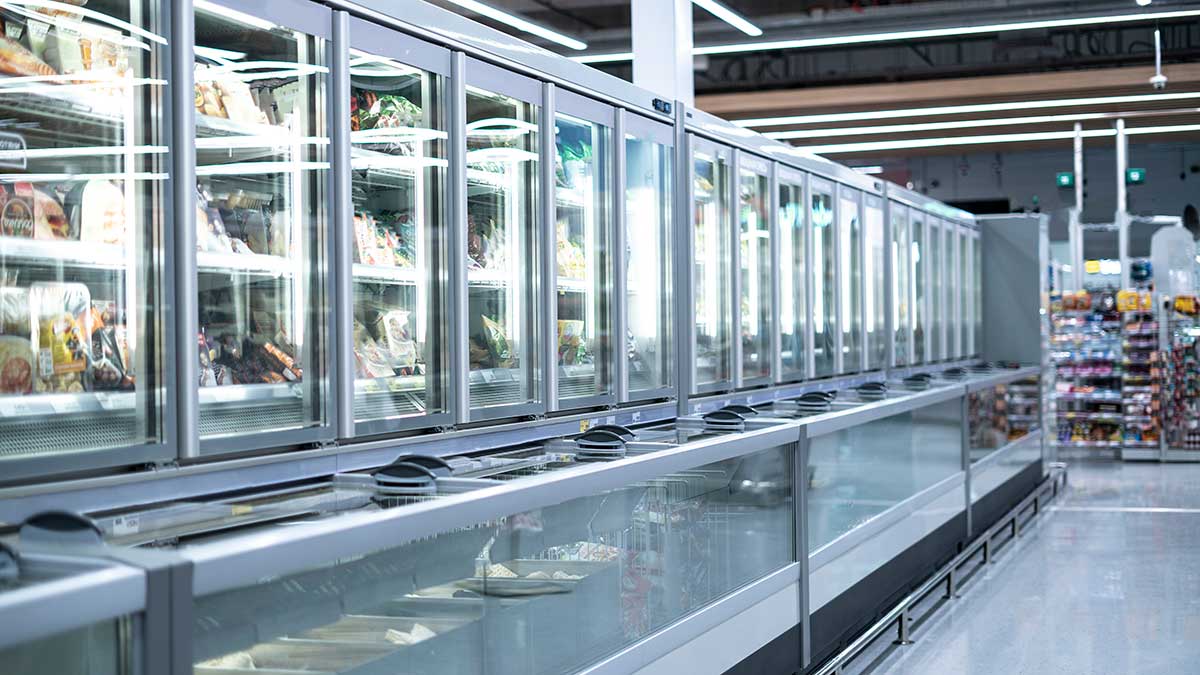
Cybersecurity experts have warned that ageing connected devices and inadequate protection for operational technology pose a growing risk to businesses, following a cyber attack that caused refrigeration systems in hundreds of French supermarkets to heat up and spoil food worth millions of euros.
The attack affected several major food retailers, including Carrefour, Intermarché, Netto, Coopérative U and Monoprix. Hackers gained control of software used to regulate refrigeration temperatures, forcing some units to heat to 50°C for six hours overnight, according to AFP.
French prosecutors have opened a cybercrime investigation into the attack, which caused food losses and equipment damage. The full extent of the incident remains unclear, as does the precise method used to gain access to the refrigeration systems.
Danish engineering company Danfoss, whose software was targeted, said the affected refrigeration units were older models that could no longer receive security updates to address the identified risk.
The incident has prompted cybersecurity specialists to warn that internet-connected equipment can remain in service long after its software support ends, leaving operators exposed to vulnerabilities they may lack the resources or expertise to address.
Vulnerabilities exposed
“This is exactly the type of story we need to be focused on,” said John Strand, Owner of Black Hills Information Security. “There is still so much focus on protecting endpoints, servers, and web applications. All of that is important. But I think some of the biggest damage we’re going to see will involve IoT devices.”
Strand said connected devices often lack regular security patches, endpoint detection and response tools, and basic network protections. Smaller businesses, in particular, may not have dedicated security teams to manage the risks.
“Once it’s sold, the expectation is that the shop that owns it is responsible for securing it. And a lot of those shops have zero information security practice,” he said.
Denis Calderone, Chief Technology Officer at Suzu Labs, said refrigeration controllers can be exposed to the internet with default credentials, weak authentication or predictable access codes.
Calderone also pointed to a demonstration by Claroty’s Team82 security research team at the DEF CON conference in August, which showed how refrigeration controls could be manipulated to disable cooling and falsify temperature readings. He said the models involved in the French incident had reached end-of-life status between 2016 and 2021, leaving operators with limited options for addressing newly discovered vulnerabilities.
“You cannot remediate your way out of this because the device manufacturer stopped supporting these at least three years ago; you can only segment it, monitor it, or replace it,” he said.
OT risks
The precise entry point used in the French attack has not been publicly established. Nevertheless, the incident has renewed attention on the risks associated with internet-facing operational technology (OT), which controls physical equipment and industrial processes.
Damon Small, a Board Member at Xcape, said businesses also needed to take responsibility for how equipment was configured and maintained, rather than assuming security could be delegated entirely to manufacturers or installation contractors.
“While threat actors remain the undeniable criminals in these incidents, operators must be held accountable for maintaining poorly configured environments,” he said. “It remains unclear whether the vendor that installed these refrigeration units also configured the software, but accountability cannot be entirely outsourced. If a criminal breaks into a house because the owner left the front door wide open, the owner shares part of the blame. To mitigate this exposure, security teams must immediately sever control interfaces from the public Internet, place maintenance access behind segmented networks requiring multifactor authentication, and apply long-available updates.”
Tamás Pentz, Head of Threat Intelligence at PCA Cyber Security, said the incident also exposed weaknesses in how organisations identify and manage the security risks of connected equipment.
“The vulnerabilities identified in these refrigeration controllers demonstrate fundamental security weaknesses: weak administrator credentials, a predictable date-based authentication code and the ability to bypass normal password verification through a crafted API request,” he said. “The bigger issue is that these devices were directly exposed to the internet without adequate firewall protection, access restrictions or network segmentation. The lack of regular security assessments, combined with outdated firmware and discontinued manufacturer support made the situation even worse.”
Connected equipment compromised
Pentz warned that similar weaknesses could affect other categories of connected equipment, including vehicles and medical devices, which may share embedded components, software libraries and communications technologies with industrial control systems.
Thomas Plank, Chief Executive of data security company Tributech, said the incident highlighted the need for safeguards at the device level, rather than relying solely on network security or user authentication.
“The freezers in around 500 French supermarkets did exactly what they were told, a command arrived (defrost, and keep defrosting) and the equipment executed it for six hours,” he said.
Plank argued that connected equipment should verify both the origin of a command and whether the requested action falls within permitted operating limits.
“Even a genuine command can be wrong; a stolen credential, a careless operator, a faulty AI writeback,” he said.
Josh Marpet, senior product security consultant at Finite State, also highlighted the importance of product security support, pointing to the EU Cyber Resilience Act and its requirements for manufacturers of products with digital elements.
There’s plenty of other editorial on our sister site, Electronic Specifier! Or you can always join in the conversation by visiting our LinkedIn page.