The EU’s Cyber Resilience Act (CRA) is forcing IoT manufacturers to rethink cybersecurity as an ongoing responsibility rather than a one-off compliance exercise, according to industry experts speaking at an IoT Insider webinar that is now available to watch on demand.
The CRA became applicable on 11 September, introducing immediate obligations around the reporting of actively exploited vulnerabilities and security incidents. The majority of the Act’s wider requirements for products with digital elements will apply from 11 December 2027, giving manufacturers a further period to prepare for the more extensive product cybersecurity requirements.
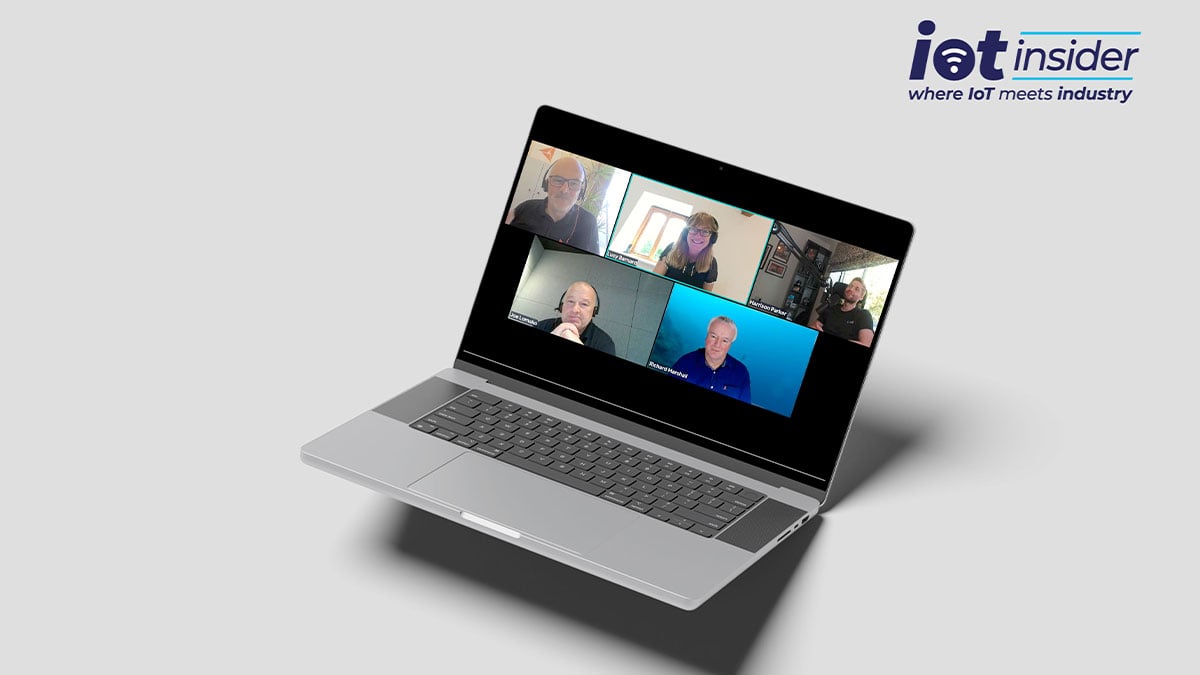
The webinar, titled ‘The Cyber Resilience Act is here: What happens next for IoT security?’, brought together David Pashley, Managing Director at Direct Insight; Joe Lomako, Cybersecurity Lab Manager at TÜV SÜD; Harrison Parker, Regional Sales Manager at QNX; and Richard Marshall, Chair of the BSI working group involved in developing the CRA’s horizontal standards.
One of the central themes of the discussion was the shift from traditional product compliance, where testing is typically carried out before a product enters the market, towards a model in which manufacturers must continue to consider cybersecurity throughout a product’s supported lifetime.
“This is far more a business problem,” said Marshall, arguing that the implications extend beyond engineering teams into procurement, product management, legal, compliance and the wider supply chain.
The change is particularly significant for IoT products, which can remain deployed for many years after they are first manufactured. Manufacturers therefore need to establish who will be responsible for monitoring vulnerabilities, assessing their impact and providing security updates long after the original engineering team has moved on to other products.
Parker highlighted one question that he said regularly exposes gaps during discussions with manufacturers: “Who is going to monitor your product in year eight?”
For manufacturers, the answer needs to be established before products are placed on the market, rather than when a vulnerability emerges years later.
The panel also warned manufacturers not to focus exclusively on new products under development.
Pashley said companies need to consider existing products that they intend to continue placing on the EU market after the wider CRA requirements take effect. Depending on the product and its architecture, meeting the requirements could require changes to hardware as well as software.
Features such as secure boot, authentication, encryption and secure updating may need to be considered at the platform level rather than added as an afterthought.
There was also discussion about the risk that manufacturers could treat the CRA primarily as a documentation and compliance exercise rather than an opportunity to improve the security of their products.
The panel argued that the underlying processes required by the regulation should increasingly become part of normal product development and management.
Lomako pointed to the need for management-level support, arguing that the breadth of the CRA means cybersecurity now involves stakeholders across the organisation rather than being an issue that can simply be handed to an engineering team.
The IoT Insider webinar, ‘The Cyber Resilience Act is here: What happens next for IoT security?’, is now available to watch on demand below.
There’s plenty of other editorial on our sister site, Electronic Specifier! Or you can always join in the conversation by visiting our LinkedIn page.